The boardroom question has changed
The first enterprise AI question was whether teams could use generative AI productively. The next is where those workloads should operate. A demonstration can run on almost any convenient service; a production system that handles confidential documents, customer information and regulated workflows must answer questions about location, access, resilience, cost and accountability.
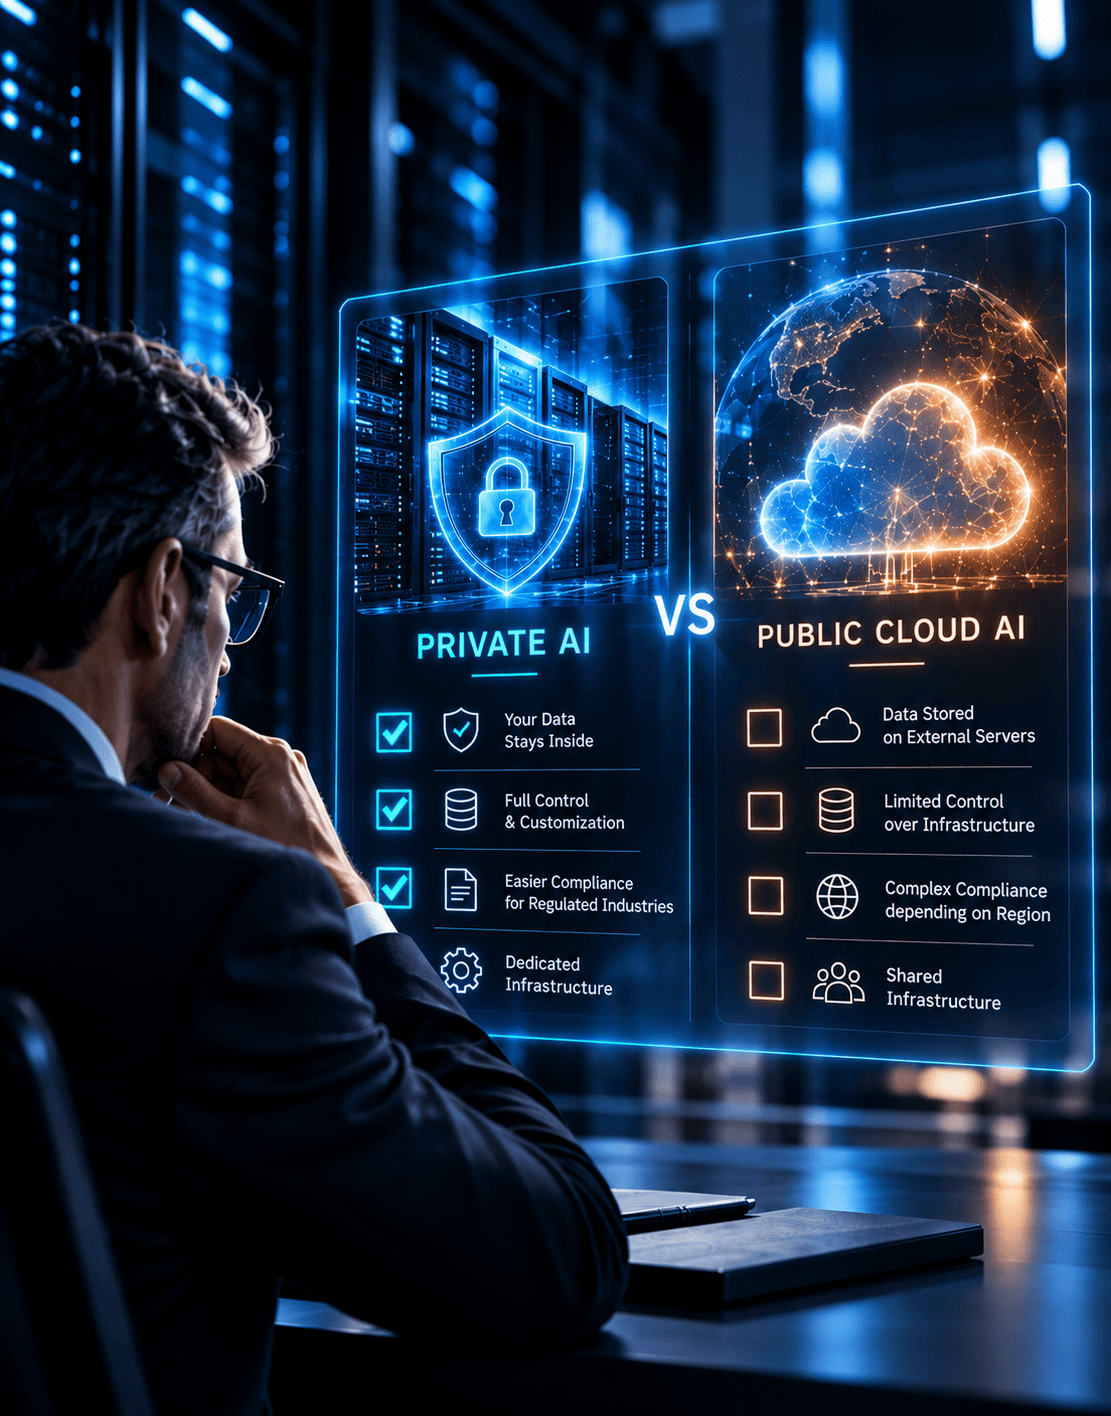
This is why private AI infrastructure has become a strategic architecture discussion rather than a niche technical preference. Private AI is not a claim that cloud AI is inherently unsafe. Enterprise cloud offerings can provide contractual protections, tenant controls and sophisticated security capabilities.
The decision is workload-specific. A customer-facing assistant working with public information may have different requirements from an internal policy copilot or a tool analyzing privileged contracts. Leaders need a method for matching each workload to an appropriate boundary.
What private AI actually means
Private AI describes an operating approach in which an organization selects and controls the environment for its AI workloads. Depending on requirements, that environment may be on-premises, private cloud, isolated or air-gapped, or part of a hybrid architecture. It is not synonymous with training a foundation model from scratch.
An organization can select a suitable model, connect approved information, operate inference within its chosen boundary and govern access to the application.
SANCTUM positions itself as a private AI platform and appliance for controlled enterprise environments. Its product architecture combines applications, orchestration, enterprise knowledge and retrieval, selected models, and organizational data. Its documented deployment options include on-premises, private cloud, air-gapped and hybrid approaches. Actual design and available capabilities should be validated against the intended configuration before procurement.
Five questions executives should settle before selecting a deployment
Which information is involved?
Classify source documents, prompts, retrieved passages, embeddings, outputs, logs and backups. A data residency statement is incomplete if it covers documents but not operational artifacts. Identify which records are confidential, regulated, privileged or business-critical and who may access each class.
Where does inference occur?
Ask whether the model runs locally or through an external service. Map every external dependency, including identity, updates, certificates, monitoring and approved integrations. Local inference can reduce exposure, but it does not by itself resolve every cross-border or security issue.
Who can operate and support the environment?
Establish administrator privileges, vendor access conditions, support approval, incident response and diagnostic handling. In the described SANCTUM appliance, there is no built-in routine vendor telemetry or remote-support channel; administrators can collect a sanitized diagnostic bundle, while engineer access requires separate authorization under the customer's process and agreement. Validate the final support design contractually.
What does the total cost include?
Compare more than model-token prices. Include compute, storage, network, integration, engineering time, patching, model evaluation, business continuity and staff training. Cloud consumption may suit variable demand; dedicated infrastructure may suit predictable or sensitive workloads. Test both with a realistic usage profile rather than a hypothetical headline price.
How will performance and risk be measured?
Define latency, answer quality, retrieval relevance, permission enforcement, uptime and recovery targets. Evaluate with representative enterprise questions and authorized user roles. A strong demo does not establish production readiness.
The governance layer is not optional
Enterprise AI governance needs to be operational. Identity and roles should determine which applications a user can access. Document and knowledge-base access controls should determine what information retrieval may surface. Retrieved content should be re-authorized against the requester rather than assuming that search results are safe.
Logging should provide useful evidence, and high-impact outputs should remain subject to human review. SANCTUM's described approach includes local inference, server-enforced roles, document and knowledge-base ACLs, private service networks and audit capability.
These measures reduce exposure; they do not guarantee breach prevention or regulatory compliance. A deployment should undergo security testing, gap remediation and verification of backup protection, privileged database access, authentication controls and audit coverage before sensitive production use.
A pragmatic pilot-to-production roadmap
Start with one measurable use case, such as searching approved policies or summarizing internal reports. Define the user group, source systems, restricted content and expected decisions. Build a small evaluation set with questions that have known answers and questions that should be refused.
Test relevance, citations, permission boundaries, latency and human review. Then test failure modes: stale documents, revoked access, service interruption, misleading prompts and recovery from backup.
The pilot should also produce a data-flow diagram and an ownership matrix. Name the business owner, platform operator, security reviewer, legal reviewer and approver for each change. Capture acceptance criteria before expansion. A successful first use case becomes a repeatable private AI foundation only when operations, controls and accountability can scale alongside users.
Where SANCTUM fits
SANCTUM's proposition is to bring approved enterprise knowledge and AI applications into an organization's selected environment, supporting knowledge assistants, document intelligence, compliance-related assistance and governed workflows.
It is an alternative delivery approach for workloads requiring locally operated inference, not a blanket replacement for ChatGPT Enterprise, Azure OpenAI or AWS Bedrock. Compare each option's actual boundary, contractual commitments and workload fit.
For the C-suite, the conclusion is not cloud versus appliance as an ideology. It is an architecture decision grounded in business value, data classification and operating responsibility. The right private AI strategy lets the organization use intelligence without treating control as an afterthought.
Does on-premises AI automatically satisfy GDPR or other regulations?
No. Technology can support a compliance program, but applicable obligations, validated controls, organizational procedures, and contracts must be assessed for each deployment.
Does private AI mean one model forever?
No. A model strategy can evolve, subject to compatibility, licensing, evaluation, and deployment requirements.